AI agent secrets management for SaaS integrations
An AI agent doesn’t need a password to cause a serious incident. One broad OAuth token, a shared API key, or an unprotected browser session
An AI agent doesn’t need a password to cause a serious incident. One broad OAuth token, a shared API key, or an unprotected browser session
A RAG feature can return a correct answer and still feel broken if users wait too long for it. For a small SaaS app, RAG
A production LLM app can look safe in a demo and still fail when it reads a hostile PDF, web page, support ticket, or tool
A shared AI runtime can be efficient, but it can also turn one weak permission check into a cross-customer data problem. AI agent multi-tenancy only

A RAG feature can look convincing in a demo and still become an expensive reliability problem in production. The real managed vs self-hosted RAG decision

Rollback is a misleading word when an AI agent has already called real tools. You can restore the agent’s state, but you can’t make an
A third-party MCP server can turn a useful AI assistant into a route through your host, client, server, and downstream systems. That convenience is exactly
An AI feature becomes expensive and unreliable the moment it can take actions without clear limits. A practical AI agent architecture gives your SaaS product
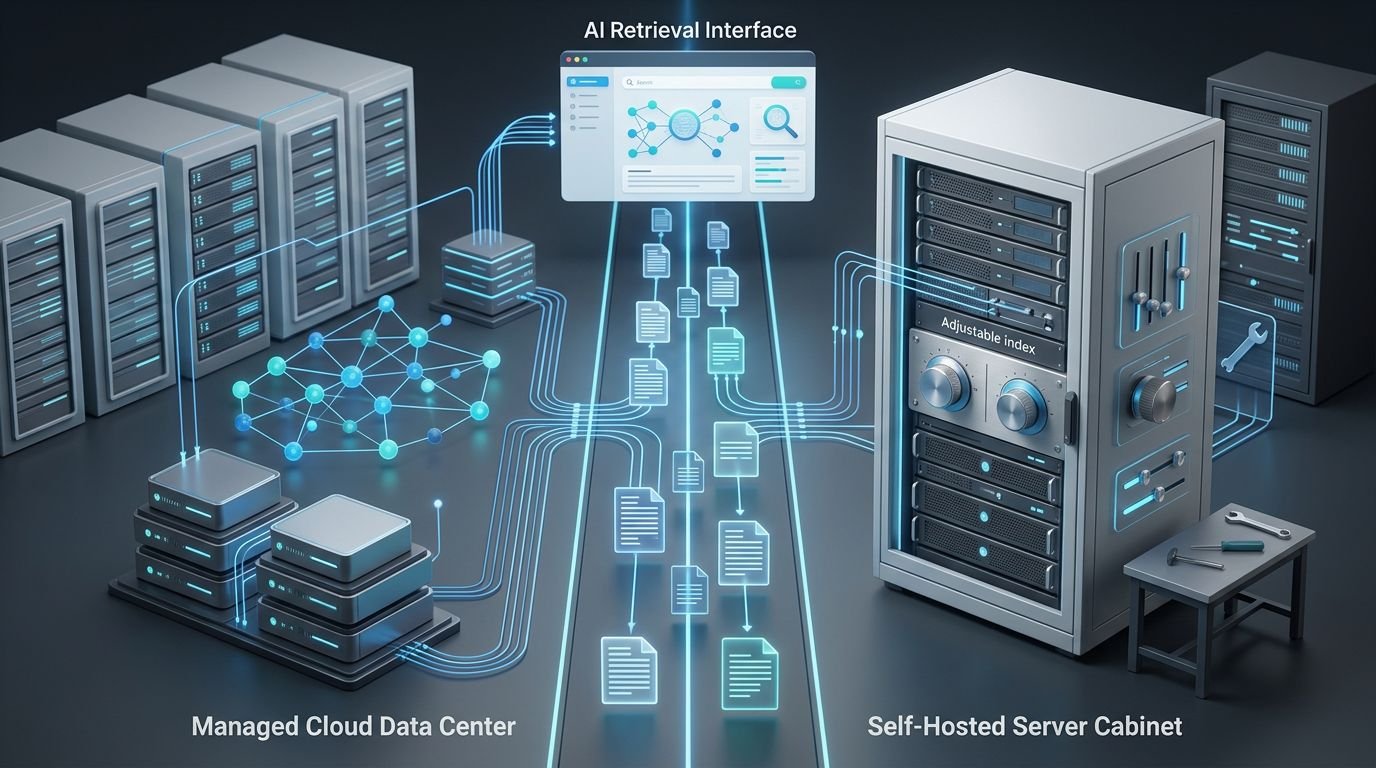
Most small Retrieval-Augmented Generation (RAG) apps don’t break because they picked the wrong vector database. They break because retrieval quality, permissions, and operating costs were
AI coding assistants can receive far more than the line under your cursor. Depending on their mode, they may see nearby files and repository instructions.